
Compliance reporting for Apple fleets.
DARE Technology · reporting and compliance for the Apple devices they manage
An Apple-focused managed service provider knew the state of every machine it looked after and had no way to show a customer any of it. We built the reporting layer over that data, and the compliance model behind the figure their customers now read.
Overview
DARE Technology manage Apple devices for their customers, on open-source tooling they had built around Munki with their own command-line agent distributing packages. The tooling did its job on the machines themselves and stopped there, because the agent wrote its output on the device and nothing stood between that output and a customer who wanted to know whether their laptops were patched.
OpenKit built Zappl, the reporting and compliance layer over the data that agent was already producing, and the first thing DARE could put in front of a customer.
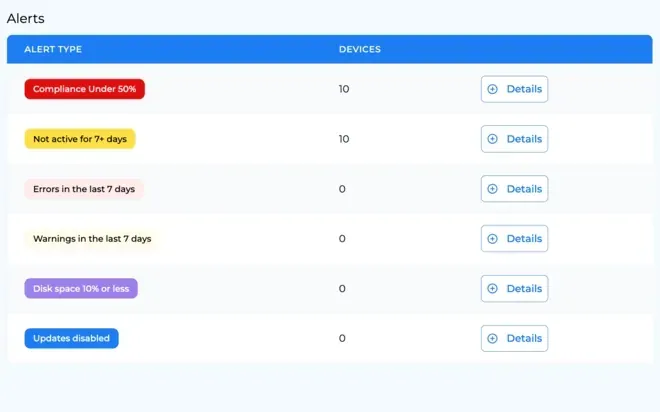
- A customer portal with device and application views, dashboards, alerts and scheduled PDF reporting by email.
- A management portal where DARE run every client, generate per-client tokens, and step into a customer’s own view to fix a problem.
- A compliance model worked out with DARE, so the figure a customer sees reflects how their devices are actually being run.
100+
customer organisations on the platform, each able to see their own devices without an engineer in the middle.
£1,000+
a month against the tooling their customers were paying for before, in many cases.
2
portals reading one set of numbers, one for DARE’s customers and one for their own engineers.
14 days
The eligibility window, applied at both device and application level.
Challenge
What DARE needed
Every conversation with a prospective client ended in the same place. How many of our machines are patched? Which ones are behind? Can we have that monthly? The honest answer was that the information existed on each device and nowhere else, so the brief went wider than a dashboard and started with what had to be true before any dashboard would mean anything:
- A customer has to be able to see their own devices, without an engineer in the middle.
- The compliance figure has to mean something, or nobody will act on it.
- DARE’s engineers need one place to run every client, or the operational cost eats the margin.
Approach
How compliance is measured
The first thing we worked out with DARE was the maths behind the figure. Pass-or-fail compliance treats a machine with one application a version behind exactly like a machine nobody has touched since spring, and a fleet scored that way tells its owner nothing they can act on.
Pass-or-fail scoring
One out-of-date application anywhere on a machine and the whole machine counts as non-compliant. Nothing else about its state matters.
A device three months out of contact scores exactly the same as a device that finished updating this morning.
Every fleet reads as broken, including the ones being managed well, so the number stops being something anyone acts on.
Averaged and eligible scoring
Compliance averaged across a device’s applications, so a machine most of the way there reads as most of the way there.
An eligibility layer on top. A device counts towards the measure only if it completed a successful full update inside the window.
A Last Compliant Date written by the agent on every run, with rules for exactly when it moves. Letting a prompted application close moves it, and deferring the prompt leaves it where it is.
The eligibility window is fourteen days, specified with the client, written into the agent and applied at both device and application level.
The build
The two portals
One record a support engineer can work from
Serial number, disk space, FileVault status, the full application list with versions and install paths, and the agent log with automatic purging. The engineer stops asking the customer to read things off their screen.

Every figure links to the devices behind it
Application counts and compliance figures are clickable throughout, filtering straight to the devices they describe. The fleet view answers "which ones?" without anyone exporting a spreadsheet to find out.

The client-management layer
DARE’s engineers create a client, generate that client’s bearer token, and keep licence keys and expiry dates against the record. When a customer hits a problem, an engineer can step into that customer’s own view of Zappl, see exactly what they are seeing, and fix it from there.

- The build: Customer portal, Client management portal, Compliance calculation model, Per-client bearer tokens, Scheduled PDF reporting, React + TypeScript.
- OpenKit certifications: ISO 27001, ISO 9001 (UKAS-accredited), Cyber Essentials.
- Controls on this project: UK GDPR, UK data residency.
ISO 27001, ISO 9001 and Cyber Essentials are OpenKit certifications, and we operate to UK GDPR. The controls listed are the ones set on this project.
Result
What changed for DARE
DARE’s customers sign in to Zappl and read the state of their own machines. OpenKit has maintained the platform since it launched, keeping patch coverage and the compliance rules current.
Both figures on this page come from DARE. Their director gives the customer count, and the saving is what their customers report against the tooling they paid for before.
Voice
What DARE said
OpenKit transformed our business requirements into Zappl, an elegant web application that provides secure Apple patch management for our customers. Their process began with thorough discovery sessions, demonstrating a clear understanding of our business objectives and user needs. The intuitive interface and streamlined workflows have reduced our staff admin workload and increased user adoption, with 100+ customers already onboarded. Throughout the partnership, OpenKit consistently demonstrated their commitment to delivering business value, from initial planning through to final implementation.
OpenKit delivered us a high-performance React application for Apple patch management, featuring large data ingestion and processing with enterprise-grade security. Their technical expertise was evident in every aspect, from an optimised frontend architecture to a robust backend with comprehensive API integration. The resulting application excels in both performance and reliability, with comprehensive monitoring and an automated deployment pipeline ensuring system stability.
Other engagements
What could your business do with AI?
Find out with experts who become part of your team. We uncover opportunities, get ideas working, and help your people build on the results. We reply within one working day.
Get in touch AI Engineering